


Security questionnaire
Reusable answers for identity, MFA, tenant isolation, encryption, auditability, integrations, deletion, backup/recovery and vulnerability-management questions.
Zeonext gives security, procurement, privacy and business stakeholders a clear view of what is implemented, what depends on the production environment, and what is not yet claimed.
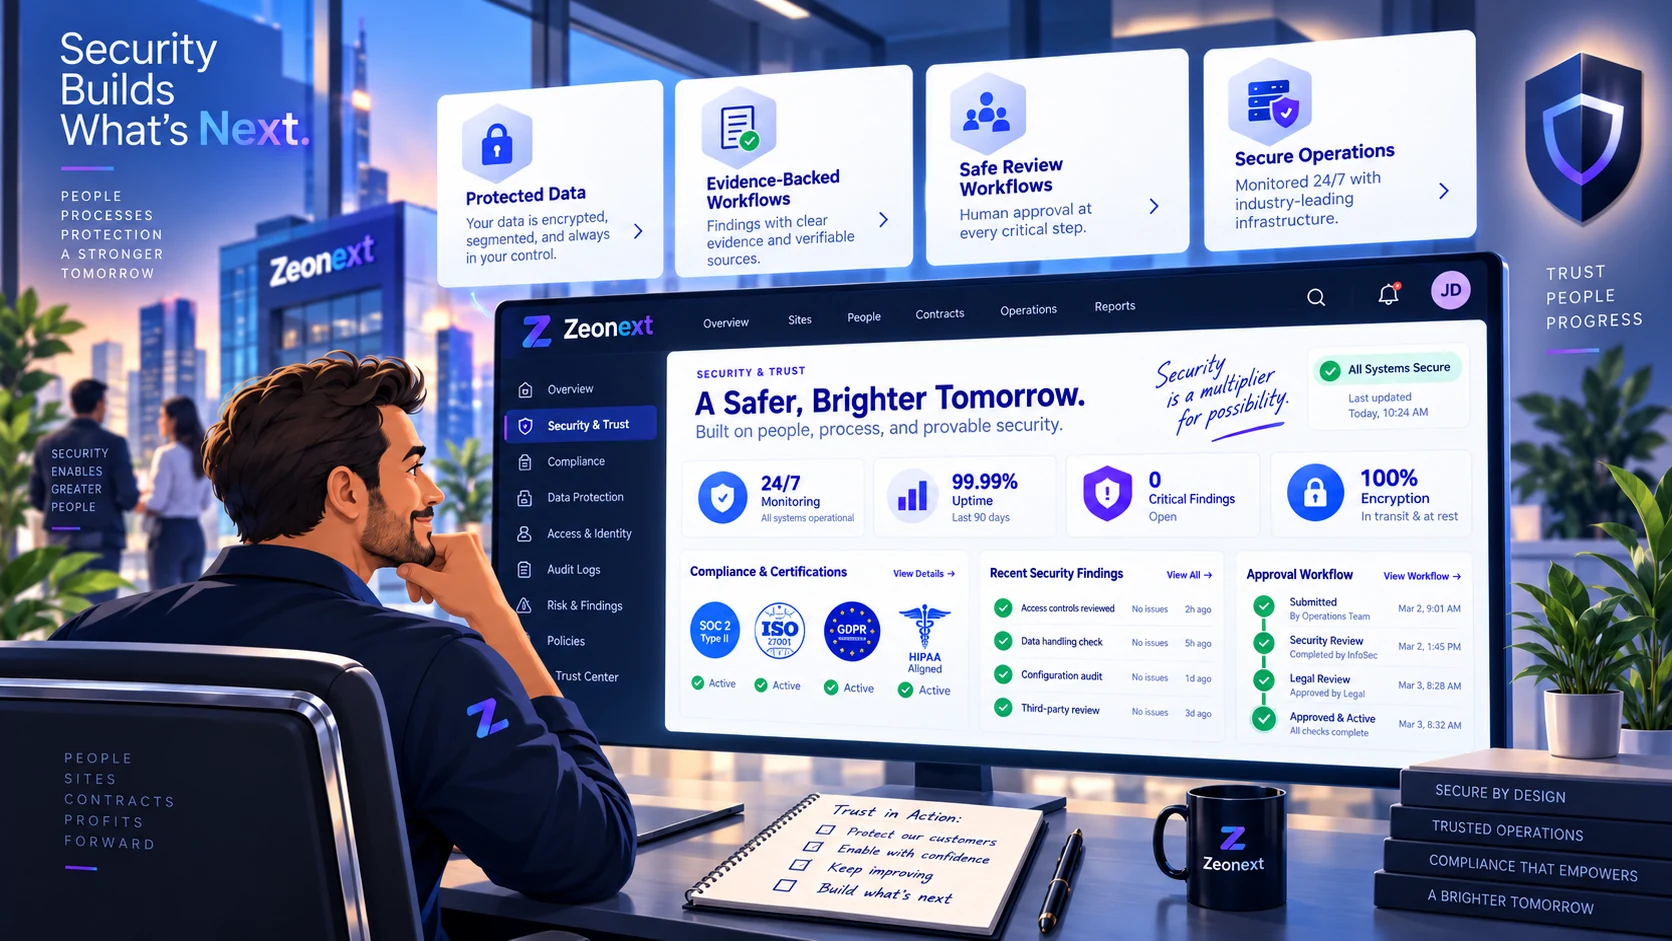
The Enterprise Trust Pack covers security controls, privacy/data handling, incident response, recovery, subprocessors, implementation assurance, procurement sequencing and framework-readiness status. It is explicitly written to prevent future-state controls from being presented as current evidence.
Reusable answers for identity, MFA, tenant isolation, encryption, auditability, integrations, deletion, backup/recovery and vulnerability-management questions.
Separates code-implemented controls from deployment evidence, organizational policy, and external attestations that are not yet claimed.
Expected data categories, temporary evidence processing, durable state, customer export boundaries, deletion and deployment-dependent residency.
Incident-response and BCP/DR operating templates with clear production exercises still required before broad rollout.
A deployment-ready register that distinguishes known configurable services from hosting/database/providers that must be finalized for production.
Order form, DPA, security questionnaire, vendor setup, billing and buyer-specific MSA/PO/privacy/BCP review can be tracked directly in the Sales Command Center.
Zeonext's release gates verify code, workflows, recovery behavior, static security contracts and built browser surfaces. Managed PostgreSQL isolation/PITR, real providers, edge TLS/headers, dependency/SBOM scans, incident drills and independent penetration testing remain production-acceptance work rather than marketing claims.
Review product security details →